FrameworkLink
Insider Threat Matrix
An open framework for computer-enabled insider threat investigations, built by the community for the community.
View
EbookPDF · 10 pagesGated
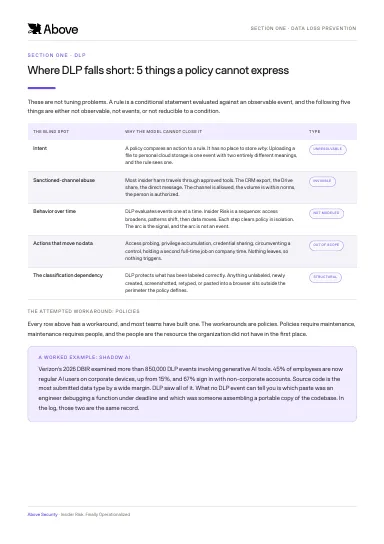
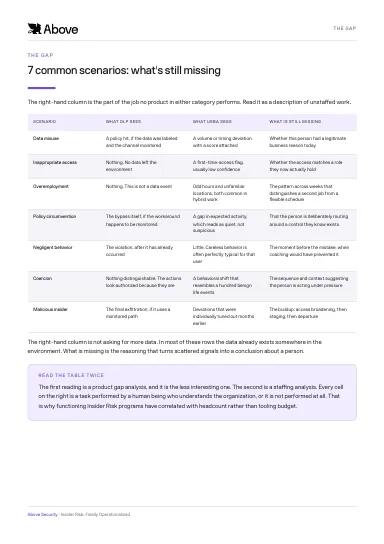
DLP and UEBA are good technologies aimed at the wrong question. Both assume Insider Risk can be specified in advance. It cannot be, because the thing being detected is a person's intent, and intent does not appear in a policy or a baseline. A walk through what each category was built for, where the model runs out of road, and why the missing capability is investigation.
Tell us where to send it. PDF · 10 pages.
FrameworkLink
An open framework for computer-enabled insider threat investigations, built by the community for the community.
View
Field guidePDF · 11 pages
Malicious, negligent, compromised, third-party, and agentic insiders: what each looks like, the early indicators, and the right response.
Get the resource
White paperLink
A maturity model, a business case, and an RFP framework for standing up an Insider Risk program.
Get the resource
We use cookies to understand how the site is used and to measure our campaigns. They are on unless you reject them. Privacy policy